The best Business Suite software in India, built to help your business grow. Contact us at +91-8882435276.
[ Contact ]
Phone number
Email address
Head office
Noida office
The right team at TriostackOne will get back to you.
Built for
SOC 2 Type II Compliance Overview
Evidence, not adjectives
Controls explained and documents shared on request

Positioning Assessment
SOC 2 is an attestation framework from the AICPA. A Type II report is written by an independent auditor and describes whether a company's controls for security, and optionally availability, confidentiality, processing integrity and privacy, operated effectively over a period. Enterprise buyers ask for it because it is evidence rather than a claim.
This page explains what a buyer should expect to review. Security architecture covers how the application, data stores and administrative access are separated. Continuous monitoring covers logging, alerting and how anomalies are reviewed. Audit reports are the auditor's documents, shared under NDA and not published here. Data encryption standards cover protection in transit and at rest. Whether a current Type II report is available, and for which period, is confirmed in writing by our team, and we will not describe a report that does not exist.
“We asked what period the report covered and whether there were exceptions. We got straight answers.”
Sample team scenario
A made-up scenario about SOC 2 Type II Compliance Overview, not a customer testimonial

All Leads
SOC 2 Type II Compliance Overview: every lead with its source, status and owner
In the Product
Imagine reading the findings instead of the brochure.
Under NDA.
Not hidden.
Never implied.
Platform Integrity
Separation of systems
Logging and alerting
Under NDA
Transit and at rest
At a Glance
What a security team should ask for.
Independent assurance
An auditor's report, with scope and period
A Questionnaire Alone: Self-declared answers
Controls
Described and testable
A Questionnaire Alone: Described as strong
Monitoring
Evidence of logging and review
A Questionnaire Alone: A statement
Exceptions
Listed in the report
A Questionnaire Alone: Not mentioned
Status
Confirmed in writing
A Questionnaire Alone: Implied
Book a walkthrough of SOC 2 Type II Compliance Overview. We set up a sandbox so you can try Security architecture, Continuous monitoring and Audit reports before you commit.
Live Interface Tour
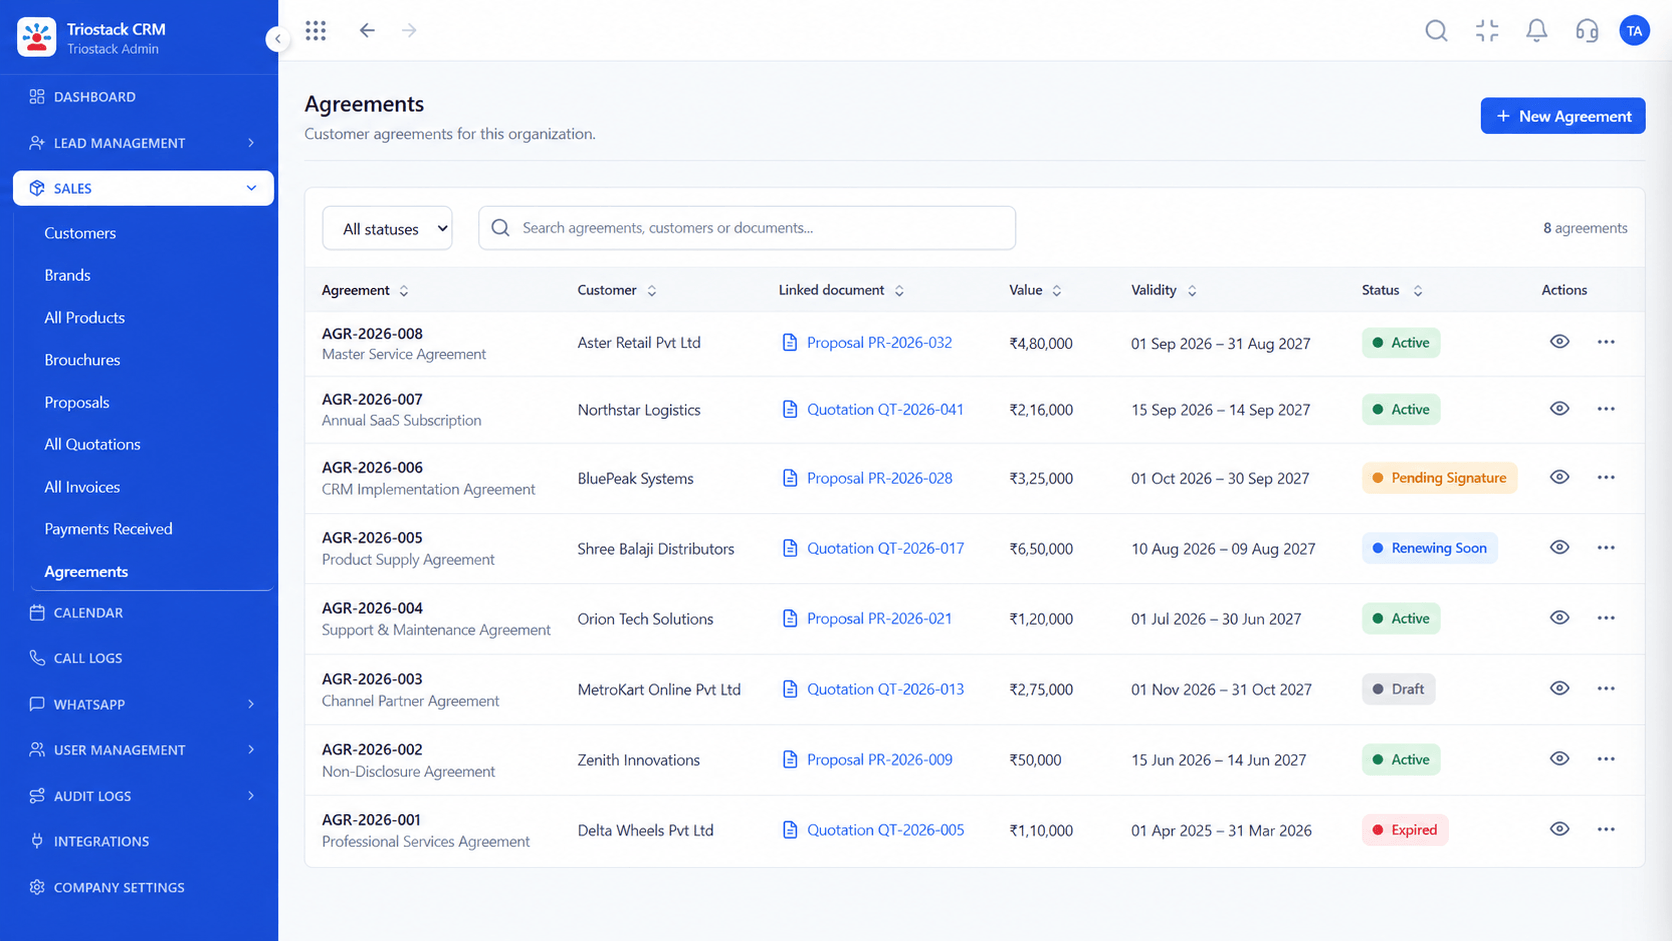
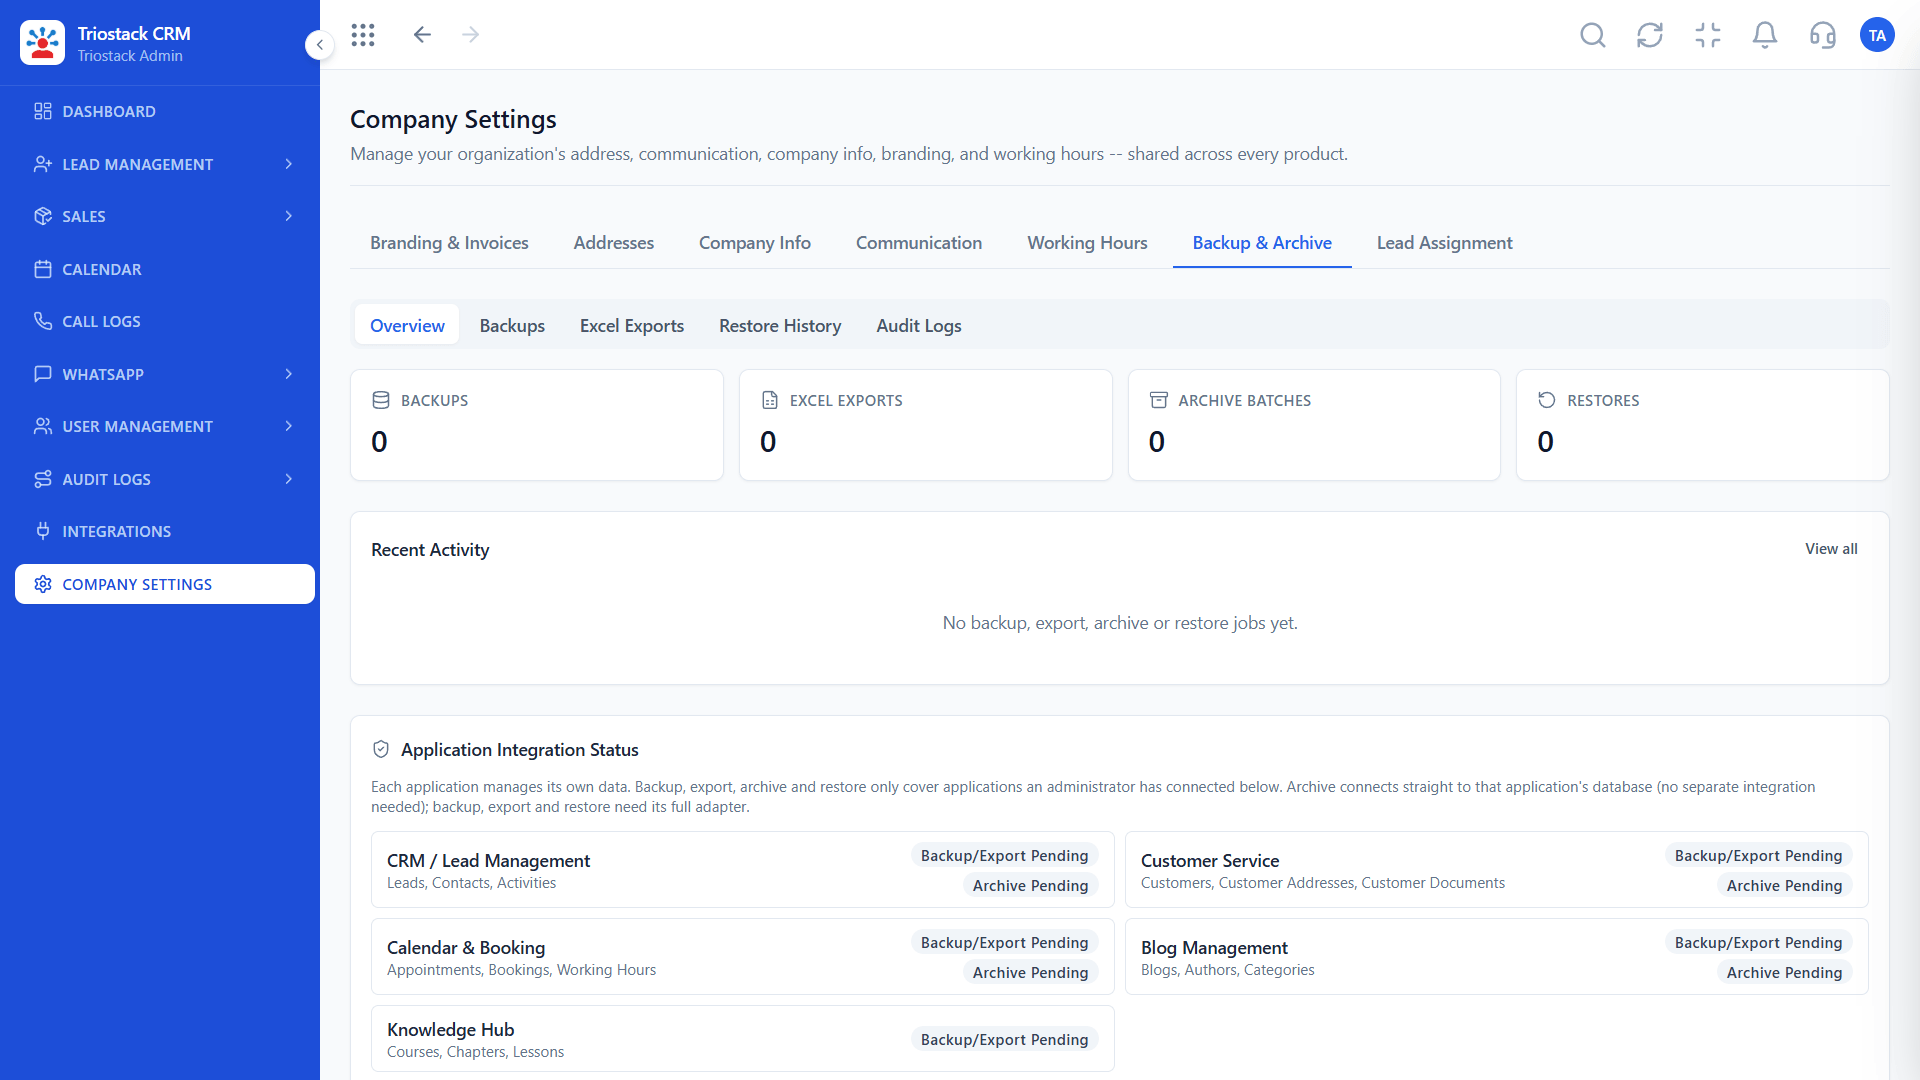
The screens below belong to SOC 2 Type II Compliance Overview: All Leads, Lead Pipeline and Sales Dashboard, all from the product.
Audit Logs
SOC 2 Type II Compliance Overview: controls explained and documents shared on request
Feature Breakdown
4 screens from the live product that show SOC 2 Type II Compliance Overview at work.
Activity records.
How it fits the plan
Ask. Request the current report and its period.
Scope. Check which trust criteria it covers.
Practical tip
Read the period and the exceptions before the opinion. A clean opinion over a short period tells you less than it seems to.

Access control.
In real life
Vendor due diligence
Security teams get documents.
Availability controls.
Watch out for
Treating a Type I report, a point-in-time design review, as proof that controls worked over time.

Authentication.
Before you start
Execution Plan
Request the current report and its period.
Check which trust criteria it covers.
Review exceptions and management responses.
Match controls to your own requirements.
Practical Guide
Before you start
A tip that helps
Read the period and the exceptions before the opinion. A clean opinion over a short period tells you less than it seems to.
A common mistake
Treating a Type I report, a point-in-time design review, as proof that controls worked over time.
Availability: What SOC 2 Type II Compliance Overview covers can depend on your plan and setup. Please confirm with our team which parts are live for your account, and any prerequisites, before you plan around it.
In Real Life
Scenario 01
Security teams get documents.
Scenario 02
Answers cite evidence.
Scenario 03
You compare periods.
Straight answers about SOC 2 Type II Compliance Overview, from setup to what happens next.
Have a question about SOC 2 Type II Compliance Overview?
Book a free callSOC 2 is an attestation report, not a certificate. Ask our team for the current status and period in writing.
Reports are shared under NDA when available.
The trust criteria and period set out in the report itself.
The security page, trust center, DPA and subprocessor list.
An overview for enterprise buyers of the controls behind SOC 2 Type II: security architecture, continuous monitoring, audit reports and encryption standards.
It runs in 4 steps: Ask, Scope, Read and Map. Request the current report and its period.
The real screens on this page include All Leads, Lead Pipeline, Sales Dashboard and Audit Logs, all captured from the product.
Request a demo and ask to see SOC 2 Type II Compliance Overview. Our team can also walk you through setup, so your first session ends with something working.
We will walk you through SOC 2 Type II Compliance Overview, from Security architecture, Continuous monitoring and Audit reports, on sample data shaped like yours.
Explore All Enterprise CRM