The best Business Suite software in India, built to help your business grow. Contact us at +91-8882435276.
[ Contact ]
Phone number
Email address
Head office
Noida office
The right team at TriostackOne will get back to you.

Positioning Assessment
Banks, NBFCs and other financial firms face expectations from their regulator on outsourcing, data location, audit trails, access control and incident handling. A CRM has to fit inside those expectations.
Triostack CRM supports banking and NBFC regulatory frameworks with controls designed for them. Customer data can be stored in India to meet data-localisation mandates. Immutable audit trails record who accessed or changed what and when, and can be exported for audit. Financial security protocols include role-based access with maker-checker approvals, encryption in transit and at rest, and multi-factor authentication for staff. Your compliance team should map these controls to the specific circulars that apply to you.
“Our auditor asked for who changed a customer's loan status. The log answered in a minute.”
Sample team scenario
A made-up scenario about BFSI Security and RBI Guidelines Compliance, not a customer testimonial

All Leads
BFSI Security and RBI Guidelines Compliance: every lead with its source, status and owner
In the Product
Imagine every control already tied to its evidence.
In India.
Immutably.
Maker-checker.
Platform Integrity
Banking and NBFC
Stored in India
Exportable
Roles, MFA, encryption
At a Glance
What a compliance team asks, and the control that answers.
| Dimension | Triostack CRM | What the Regulator Expects |
|---|---|---|
| Data location | Customer data stored in India | Data kept in the country |
| Audit trail | Immutable, exportable log of access and changes | Complete, reviewable records |
| Access control | Roles with maker-checker approvals | Segregation of duties |
| Authentication | Multi-factor for staff | Strong authentication |
| Encryption | In transit and at rest | Data protection |
Book a walkthrough of BFSI Security and RBI Guidelines Compliance. We set up a sandbox so you can try Regulatory frameworks, Data localisation and Audit trails before you commit.
Live Interface Tour
The screens below belong to BFSI Security and RBI Guidelines Compliance: All Leads, Lead Pipeline and Lead Follow-Ups, all from the product.
Audit Logs
BFSI Security and RBI Guidelines Compliance: localised data, audit trails and access control
Feature Breakdown
4 screens from the live product that show BFSI Security and RBI Guidelines Compliance at work.
Who did what.
How it fits the plan
Map. List the circulars and the controls each needs.
Configure. Set roles, maker-checker and authentication.
Practical tip
Keep a table of regulatory expectation, control and evidence. It is the first thing an auditor asks for.

Access by role.
How it fits the plan
Configure. Set roles, maker-checker and authentication.
Evidence. Export audit logs and configuration for your file.
In real life
Regulatory audit
You show controls and logs.

Who has access.
How it fits the plan
Evidence. Export audit logs and configuration for your file.
Review. Have compliance sign off before go-live.
Watch out for
Treating a vendor's support for a framework as your own compliance. Responsibility stays with the regulated firm.
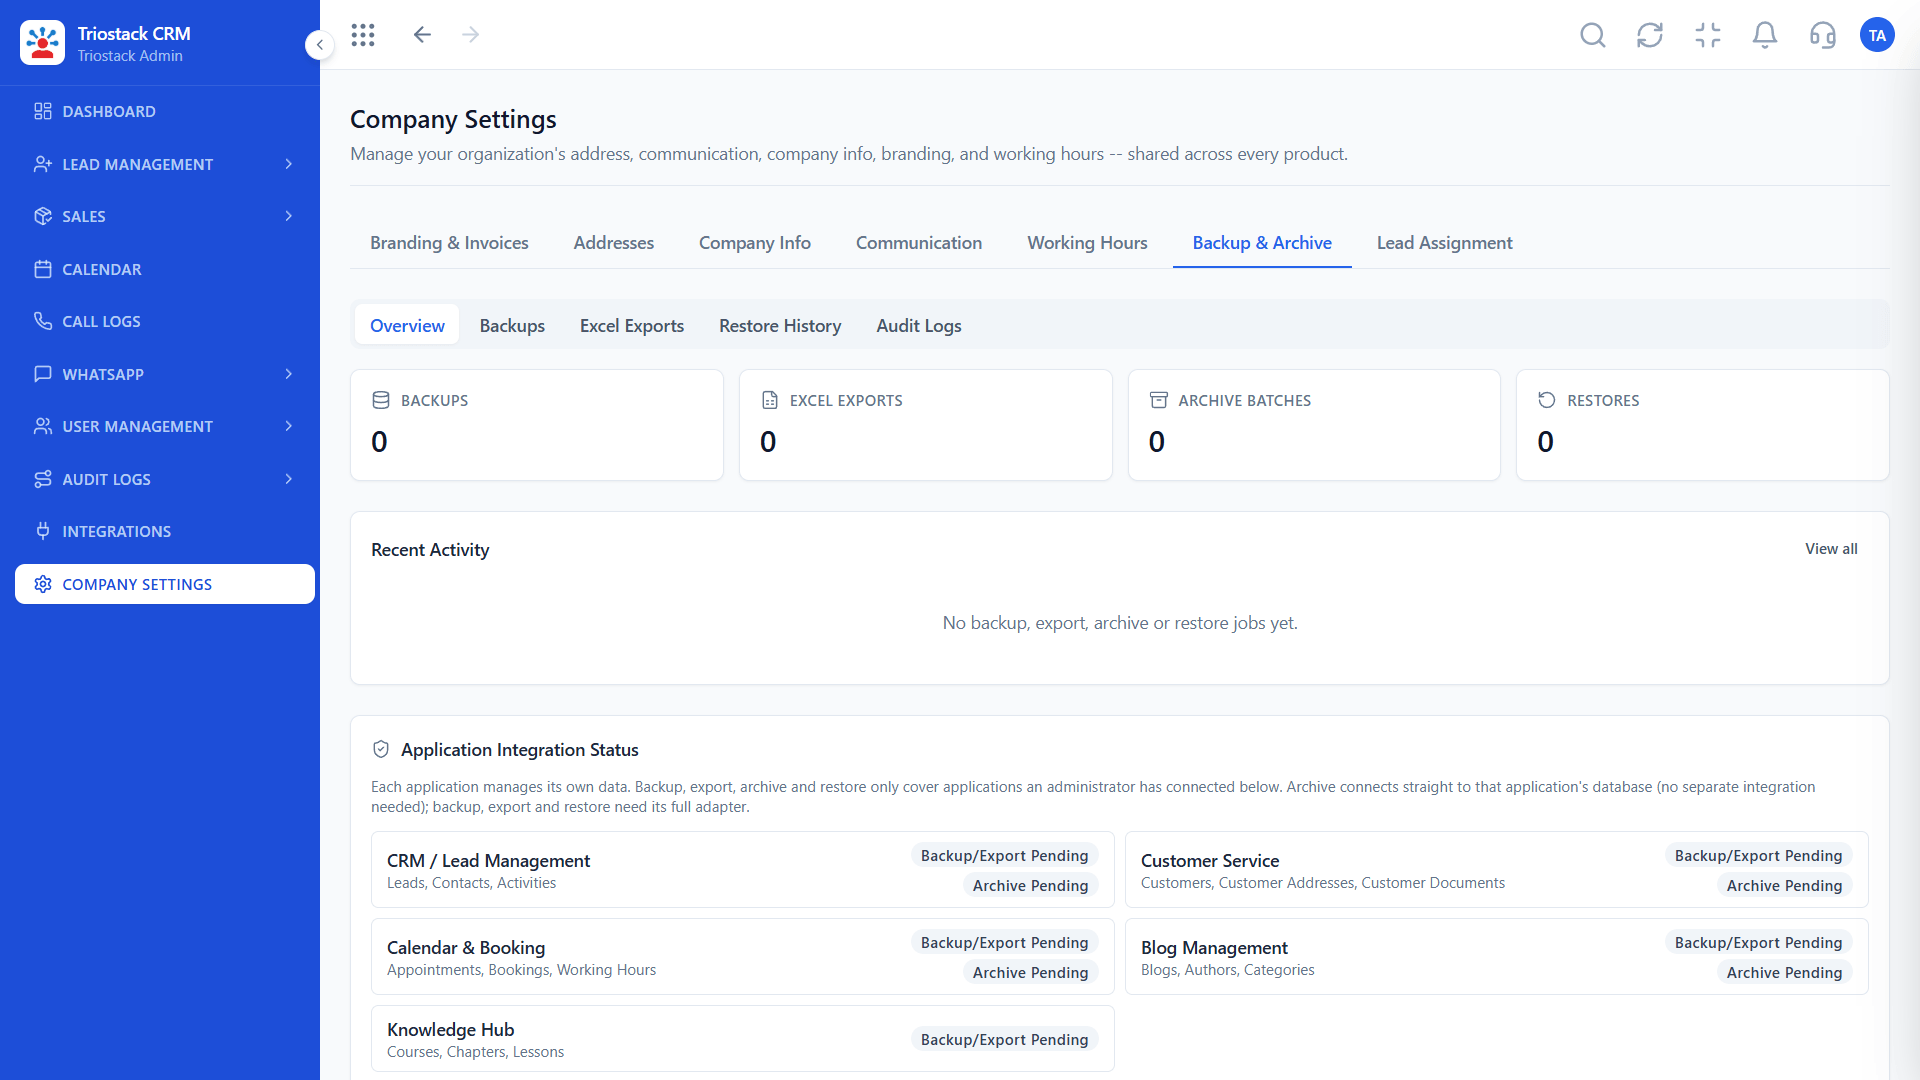
Recovery settings.
How it fits the plan
Review. Have compliance sign off before go-live.
Map. List the circulars and the controls each needs.
Before you start
Execution Plan
List the circulars and the controls each needs.
Set roles, maker-checker and authentication.
Export audit logs and configuration for your file.
Have compliance sign off before go-live.
Practical Guide
Before you start
A tip that helps
Keep a table of regulatory expectation, control and evidence. It is the first thing an auditor asks for.
A common mistake
Treating a vendor's support for a framework as your own compliance. Responsibility stays with the regulated firm.
Availability: What BFSI Security and RBI Guidelines Compliance covers can depend on your plan and setup. Please confirm with our team which parts are live for your account, and any prerequisites, before you plan around it.
In Real Life
Scenario 01
You show controls and logs.
Scenario 02
Access is set before go-live.
Scenario 03
The mapping is already done.
Straight answers about BFSI Security and RBI Guidelines Compliance, from setup to what happens next.
Have a question about BFSI Security and RBI Guidelines Compliance?
Book a free callIt provides controls designed to support them. Your compliance team maps them to the circulars that apply to you.
Yes, customer data can be stored in India for data-localisation needs.
Yes, an immutable log of access and changes that can be exported.
Yes, for staff accounts.
How Triostack CRM supports banks and NBFCs: regulatory framework alignment, data localisation, audit trails and financial security protocols for RBI-regulated firms.
It runs in 4 steps: Map, Configure, Evidence and Review. List the circulars and the controls each needs.
The real screens on this page include All Leads, Lead Pipeline, Lead Follow-Ups and Audit Logs, all captured from the product.
Request a demo and ask to see BFSI Security and RBI Guidelines Compliance. Our team can also walk you through setup, so your first session ends with something working.
We will walk you through BFSI Security and RBI Guidelines Compliance, from Regulatory frameworks, Data localisation and Audit trails, on sample data shaped like yours.


