The best Business Suite software in India, built to help your business grow. Contact us at +91-8882435276.
[ Contact ]
Phone number
Email address
Head office
Noida office
The right team at TriostackOne will get back to you.
Built for
HIPAA Compliant Medical CRM
Enquiry to appointment
Patient data handled with controls

Positioning Assessment
Healthcare providers get enquiries about doctors, tests and appointments, usually by phone and WhatsApp, and follow up on missed calls and booked slots. These conversations contain patient information, which brings legal duties.
Triostack CRM stores electronic protected health information encrypted, and limits who can see it with role-based access controls, so a receptionist, a doctor and a billing officer each see only what they need. Every access and change is recorded in the audit log. Business associate agreements are available for healthcare customers who need one. Patient enquiries are handled through secure forms and a shared inbox, with appointments booked on the calendar and reminders sent to the patient.
“The receptionist could book appointments but could not open clinical notes. The audit log showed who looked at what.”
Sample team scenario
A made-up scenario about HIPAA Compliant Medical CRM, not a customer testimonial

Lead Pipeline
HIPAA Compliant Medical CRM: drag deals across your own sales stages
In the Product
Imagine every patient detail guarded, and every glance recorded.
PHI protected.
Need-to-know.
BAA available.
Platform Integrity
Stored encrypted
By role
Available on request
Forms and shared inbox
At a Glance
What changes when patient data has safeguards.
Patient data storage
Encrypted
A Shared Spreadsheet: In a file anyone can open
Who can see what
Role-based access controls
A Shared Spreadsheet: Everyone sees all
Accountability
Audit log of access and changes
A Shared Spreadsheet: None
Agreement
BAA available
A Shared Spreadsheet: None
Patient enquiries
Secure forms and shared inbox
A Shared Spreadsheet: Personal phones
Book a walkthrough of HIPAA Compliant Medical CRM. We set up a sandbox so you can try Encrypted PHI, Access controls and BAA agreements before you commit.
Live Interface Tour
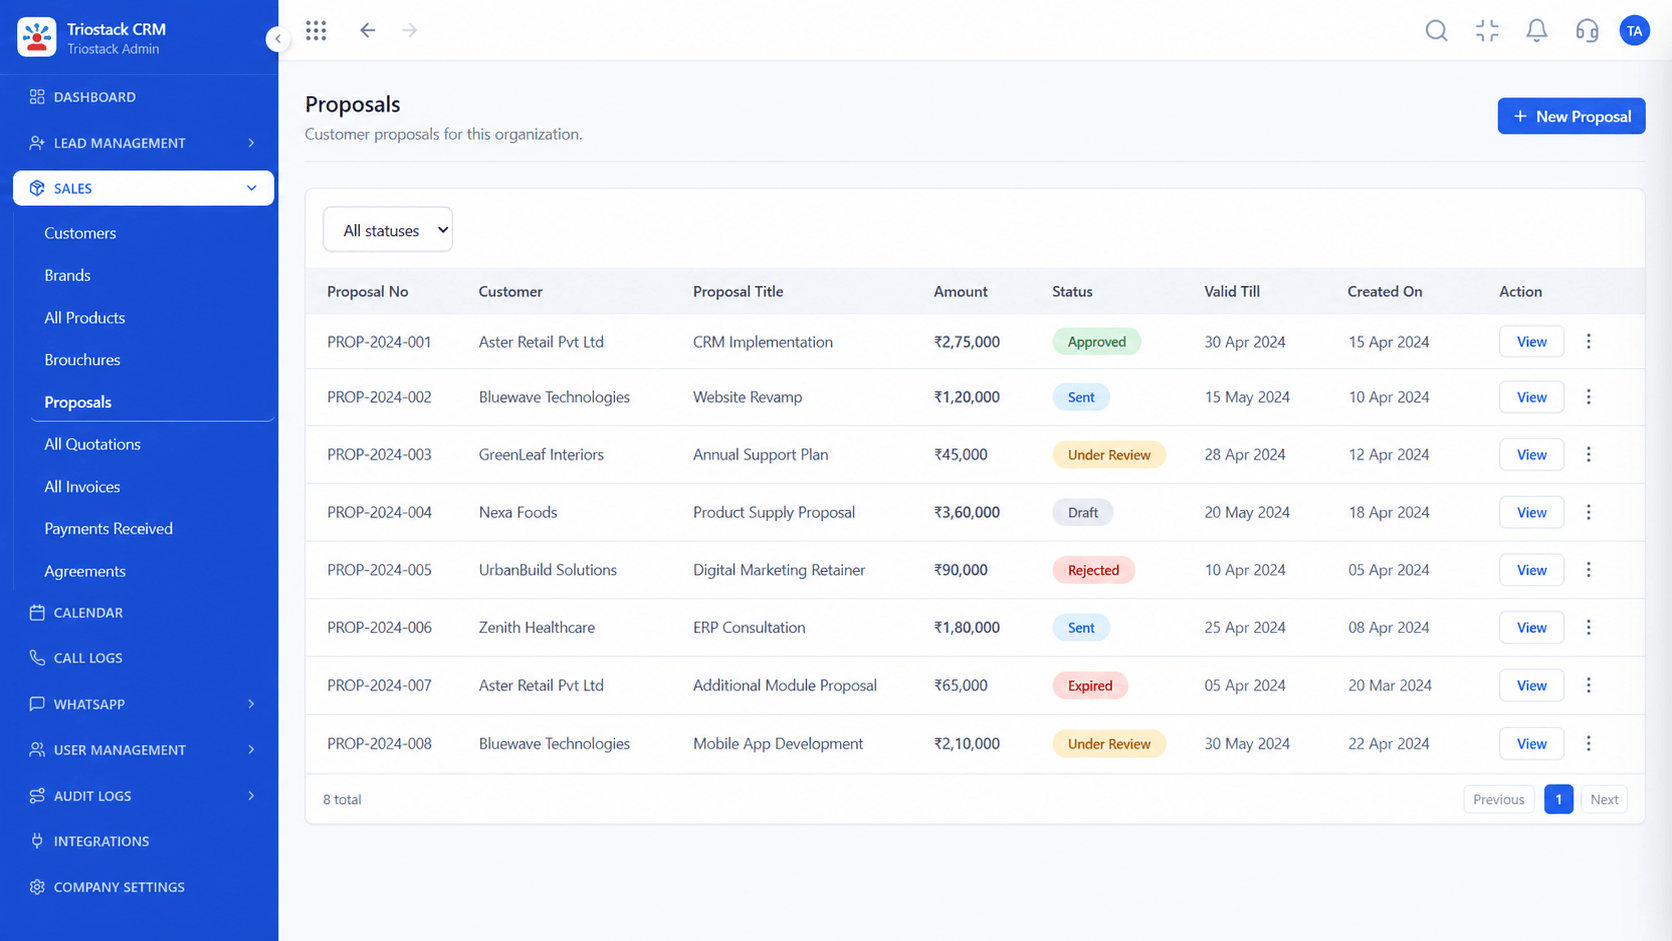
The screens below belong to HIPAA Compliant Medical CRM: Lead Pipeline, Call Logs and WhatsApp Team Inbox, all from the product.
Calendar & Bookings
HIPAA Compliant Medical CRM: patient data handled with controls
Feature Breakdown
4 screens from the live product that show HIPAA Compliant Medical CRM at work.
Appointments.
How it fits the plan
Agree. Put the business associate agreement in place.
Roles. Define roles for front desk, clinical and billing staff.
Practical tip
Write down which staff need to see clinical details and which do not, then set roles to match.

Who sees what.
In real life
Missed calls
Each gets a follow-up.

Who accessed what.
Watch out for
Giving every staff member the same access because it was quicker to set up.

Patient enquiries.
Before you start
Execution Plan
Put the business associate agreement in place.
Define roles for front desk, clinical and billing staff.
Receive enquiries through secure forms.
Check the audit log regularly.
Practical Guide
Before you start
A tip that helps
Write down which staff need to see clinical details and which do not, then set roles to match.
A common mistake
Giving every staff member the same access because it was quicker to set up.
Availability: What HIPAA Compliant Medical CRM covers can depend on your plan and setup. Please confirm with our team which parts are live for your account, and any prerequisites, before you plan around it.
In Real Life
Scenario 01
Each gets a follow-up.
Scenario 02
Enquiries get an owner.
Scenario 03
The audit log shows access.
Straight answers about HIPAA Compliant Medical CRM, from setup to what happens next.
Have a question about HIPAA Compliant Medical CRM?
Book a free callIt is built for healthcare use, with encrypted PHI, role-based access controls and audit logs. Compliance also depends on how your organisation uses it.
Yes, business associate agreements are available for healthcare customers.
Yes, stored PHI is encrypted.
Only the roles you allow, with access recorded in the audit log.
A CRM for healthcare providers: encrypted electronic PHI storage, access controls, BAA agreements and secure handling of patient enquiries and appointments.
It runs in 4 steps: Agree, Roles, Capture and Review. Put the business associate agreement in place.
The real screens on this page include Lead Pipeline, Call Logs, WhatsApp Team Inbox and Calendar & Bookings, all captured from the product.
Request a demo and ask to see HIPAA Compliant Medical CRM. Our team can also walk you through setup, so your first session ends with something working.
Keep Exploring
We will walk you through HIPAA Compliant Medical CRM, from Encrypted PHI, Access controls and BAA agreements, on sample data shaped like yours.
Explore All Industry CRM